Nginx reverse proxy in front of several WordPress servers
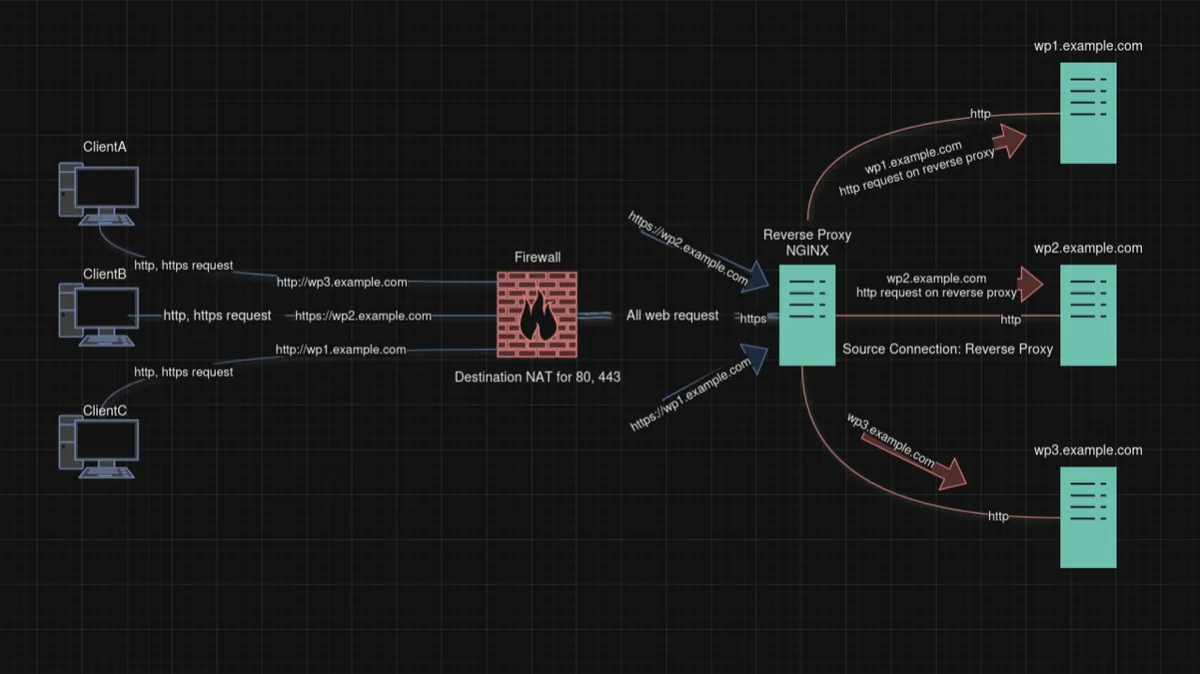
I route HTTP and HTTPS traffic for three WordPress servers in a DMZ through a single Nginx reverse proxy. TLS terminates at the proxy while the backends keep serving plain HTTP.
What the article covers
- Installing Nginx on Debian and disabling the default site
- A separate sites-available config per domain: listen on port 80, Host, real IP, X-Forwarded-For/Proto/Server headers and proxy_pass
- sites-enabled links and restarting Nginx
- Let's Encrypt certificates per domain with the Certbot Nginx plugin
- Verifying automatic renewal with a certbot dry run and the certbot.timer unit
- Separating the web DMZ from the server DMZ on a Palo Alto firewall, with destination NAT